Law No. 124/2024 · GDPR · ISO/IEC 27001 · SOC 2
GDPR and data protection in Albania, without surprises.
MH Consulting helps banks, companies and institutions in Albania comply with Law 124/2024 and the GDPR: from the initial assessment to policies, the DPO role and audit.
- SOC engagements delivered
- 80+
- Audit, GRC, IT, cyber & privacy projects
- 500+
- International qualifications held
- 80+
Services
Compliance, security and audit under one roof
The services clients ask us for most. Each has its own page with the scope, the steps and what we deliver.
Law 124 and GDPR Compliance
Data mapping, record of processing activities, policies, DPIAs and readiness for an inspection by the Commissioner.
- Gap analysis
- DPIA
- Ligji 124/2024
- GDPR
Data Protection Officer (DPO)
Outsourced DPO: advice, monitoring and a contact point for the Commissioner.
Learn moreISO 27001 Implementation and Audit
ISMS design, risk management, Annex A controls and certification support.
Learn moreSOC 1, SOC 2 and SOC 3 Reports
Attestation, readiness and training ahead of the engagement.
Learn morePenetration Testing and Red Teaming
Testing of infrastructure, web, mobile and cloud, with technical and executive reports.
Learn moreIT Audit
Audits against COBIT, NIST and the requirements of local regulators.
Learn moreMore practice areas
- Cybersecurity and Resilience
- AI Compliance and Security
- Governance, Risk and Compliance (GRC)
- Cloud Security Architecture
- SOX and J-SOX Compliance
- ESG and Sustainability Reporting
- IT Strategy and Service Management
How we work
From assessment to audit readiness
- 1
Assess
Data mapping and risk assessment: where you stand today against the law and the standard.
- 2
Document
Policies, procedures and records written for your organization.
- 3
Implement
Putting controls in place and training the staff who use them every day.
- 4
Audit
Independent review and readiness for certification or inspection.

Independent advisors. Trusted by regulated industries across Europe, the Balkans and the Middle East.
About us
Local delivery, international methodology
MH Consulting operates across Albania and the wider Balkan region, delivering specialized services in IT Governance, Risk and Compliance (IT GRC), Information Systems Auditing, and information security for regulated industries — with over 10 years of hands-on experience in IT audit within the banking sector and other highly regulated environments.
Through an exclusive cooperation agreement with a UK-headquartered advisory firm with offices in Poland and the UAE, we combine strong local execution with international methodologies, frameworks and assurance standards — supporting clients across finance, energy, ICT and the public sector.
- Region
- Balkans
- Partner HQ
- London, UK
- Partner Offices
- Poland · UAE
- Cooperation
- Exclusive
Our Competencies
International certifications held by our team
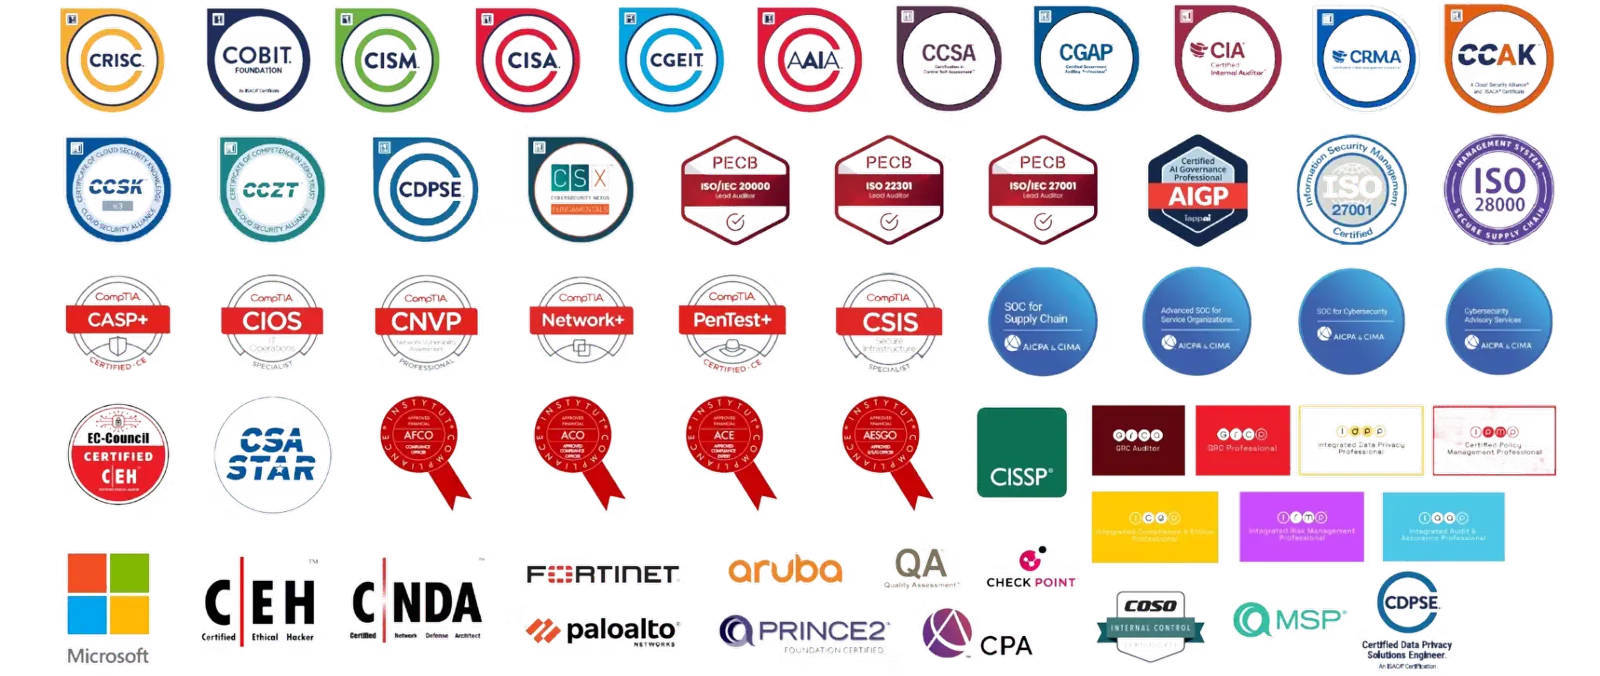
- CISA
- CISM
- CRISC
- CGEIT
- CDPSE
- CISSP
- CIA
- CRMA
- AIGP
- CCSK
- CCAK
- CEH
- ISO/IEC 27001 Lead Auditor
- ISO 22301 Lead Auditor
- ISO/IEC 20000 Lead Auditor
- CompTIA CASP+
- CompTIA PenTest+
- PRINCE2
Articles
Latest articles
What a DPO does: duties, independence and limits
What a Data Protection Officer (DPO) does: the main duties, why the role must be independent and what is not the DPO's responsibility.
Read the articleData subject requests: how to respond
How to respond to requests for access, correction or erasure of personal data: a five-step process and the mistakes to avoid.
Read the articleFrequently asked questions
Law 124 and data protection in Albania
Can't find your answer? Write to us and we will reply within one business day.
Ask a questionHow is personal data protection regulated in Albania?
Personal data protection in Albania is governed by Law No. 124/2024, which is fully aligned with the GDPR. Every organization that processes personal data must apply the principles of lawfulness, minimization, security and accountability, and identify a legal basis for each processing activity.
Who is the Albanian Data Protection Commissioner?
The Information and Data Protection Commissioner (IDP) is the supervisory authority in Albania. It oversees the application of Law 124/2024, carries out inspections, handles complaints and imposes administrative sanctions on controllers and processors that breach the law.
How do we prepare for an inspection by the Commissioner?
To be ready for an inspection, MH Consulting recommends: (1) a GDPR / Law 124 gap analysis, (2) a record of processing activities, (3) privacy policies and internal procedures, (4) DPIAs for high-risk processing, (5) staff training, (6) appointing a DPO, (7) an incident response plan with notification within 72 hours, and (8) periodic compliance audits.
What does GDPR compliance mean in Albania, and how does it relate to Law 124?
GDPR in Albania is applied through Law No. 124/2024 on personal data protection. MH Consulting provides gap analysis, records of processing activities, DPIAs, policies, training and the DPO role for full GDPR compliance in Albania.
What is Law 124 and how does MH Consulting help?
Law 124/2024 regulates personal data protection in Albania and aligns the framework with the GDPR. MH Consulting provides gap assessments, policies, the record of processing activities, DPIAs, training and the DPO role.
Do you provide ISO 27001 implementation and certification support?
Yes. We cover gap analysis, ISMS design, risk management, policies, Annex A controls, internal audit and support through ISO/IEC 27001 certification.
What is the difference between SOC 1 and SOC 2?
SOC 1 focuses on controls that affect clients' financial reporting, while SOC 2 covers the Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality and Privacy.
What does a penetration test from MH Consulting include?
Penetration testing of infrastructure, web, mobile and cloud, following OWASP/PTES methodology, with a technical and an executive report and a retest after remediation.
Do you perform IT and cyber security audits?
Yes. IT audits, cyber security assessments, and compliance with international frameworks (NIST, ISO 27001, COBIT) and local regulators.
Let's talk about your next engagement.
Tell us about your engagement — we typically respond within one business day.